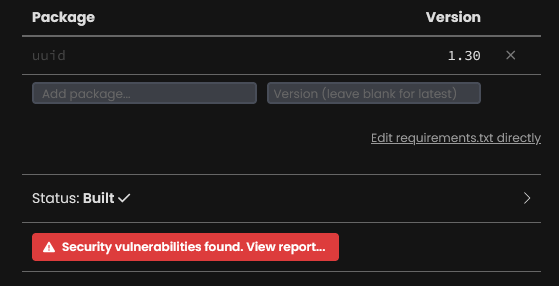
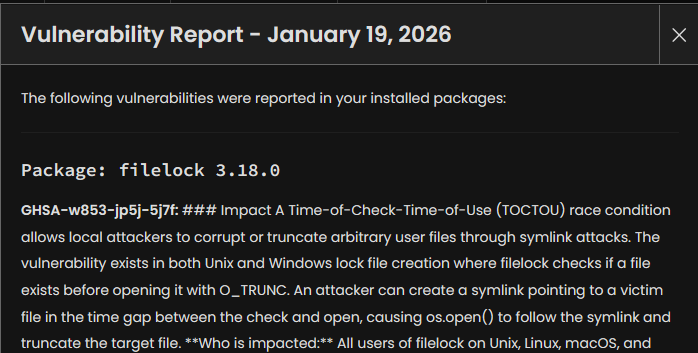
I created the app at January 30 2026. Why do i see this warning? Is the warning connected to the package uuid? When so how can i see this connection? Is this something i can fix? When so how can i do this? Where can i find information about this topic in the docs?
i did tutorials and loaded the plant shop example (i only joined anvil at 16 January 26). In the mentioned app i only added uuid as package and this was the first and only package so far which i added. I checked the existing (tutorial) projects but i dont see a package named filelock.
after four days, still no developer feedback on a security-related issue. Since this is quite a sensitive issue, I would like to have it resolved quickly. I have not installed a package called filelock at any point. So why am I getting the error message?
Since I have not installed it, could it be interfering with another project? If that is the case, I would like to know so that I can stop working on it. If it is my mistake, it would be nice to get some feedback from the developers.
I find it surprising that there has been no response from them. If a post mentions a security vulnerability, I would expect a quick response.
What can I expect if it is a productive program and such messages appear? It does not inspire confidence, especially since I am developing a compliance tool.
I’m sorry if I sound a little harsh, but if I plan to commit to a tool in the future, the framework conditions have to be right. And security is a key indicator for me.
When you install custom Python packages, we start from a base image with a (small) number of packages already installed. The base images get updated from time to time as required, and it looks like a new vulnerability has been reported in a package installed in those base images since the last update. The vulnerability scan is done on every build, so you can be sure you know exactly what’s going on in the server environment your code runs in. We don’t, for example, suppress CVEs just because they’re part of the base image and (as in this case) pose no risk. In the future we’ll likely provide commentary alongside these reports, but for now we just make the raw data available.
We’ll release new base images soon, which will update the affected packages, and of course we do this quickly when a vulnerability that might affect people’s apps is identified. I can confirm that this particular CVE is not a problem - the attacker would have to have access to the filesystem of your server environment. In the meantime you could always manually add filelock 3.21.2 to your custom packages, which will force an upgrade and resolve that particular issue.
I should also confirm that there is no cross-talk between environments - every App Environment using Python 3.10 has its own isolated server environment.
Now i added filelock 3.21.2 and the security issue für filelock disappeared. But then appeared new warnings: pip 25.1.1 and urllib3 2.4.0
After adding them too with the latest version the warnings are gone.
But what do i need them for? I dont want to add packages which are not neccessary for my project to avoid security issues.
Hello @de_maggus,
Anvil requires a small number of Python packages to run, and pip and urllib3 are included as part of the base environment. You can find more information here: Anvil Docs | Installing Custom Packages